countdown| contador | timer Ferramentas!
Pressione o botão copiar e colar no seu blog ou website.
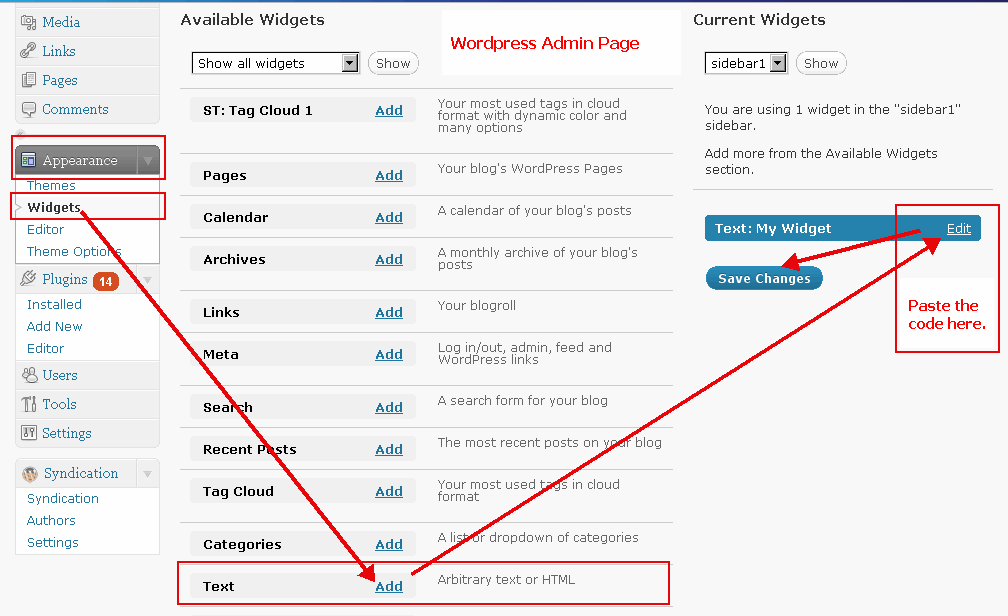
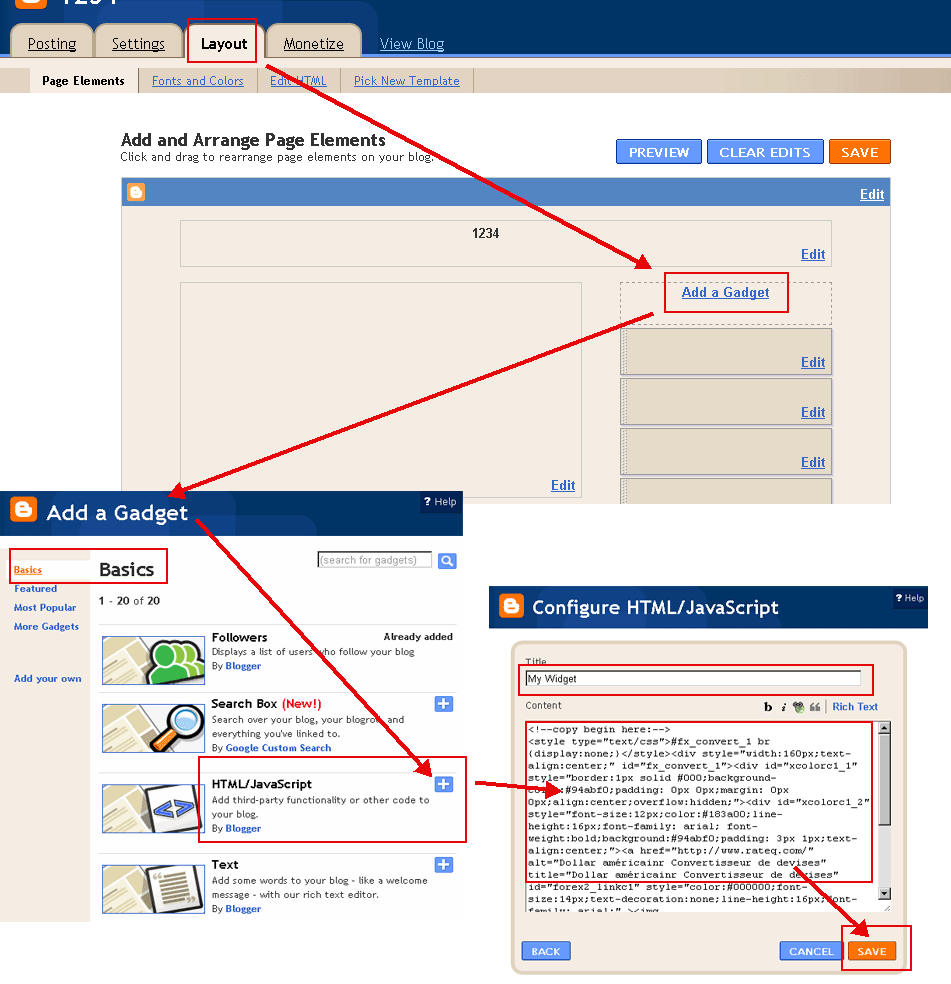
(Por favor mudar para o modo HTML ao postar em seu blog. Exemplos: Exemplo WordPress, Exemplo Blogger)
Support | Cyber Security Updates - AVEVA AVEVA Group Limited on behalf of itself and its subsidiaries (“AVEVA”) is releasing a security update to address vulnerabilities impacting AVEVA PI Integrator for Business Analytics, version 2020 R2 SP1 and all prior
SECURITY BULLETIN AVEVA-2026-005 For step-by-step instructions on where and how to apply these configuration settings, how to migrate HMI displays, compatible server-client versions list, and additional details please refer to KB117814 “AVEVA Midstream Product Bulletin – Removal of Binary Formatter”
AVEVA Pipeline Integrity Monitor - CISA Successful exploitation of these vulnerabilities could allow an attacker to disclose information, brute-force hashes, or run arbitrary code in a browser session The following versions of AVEVA Pipeline Integrity Monitor are affected:
AVEVA Group Limited, Security Bulletin AVEVA recommends that organizations evaluate the impact of these vulnerabilities based on their operational environment, architecture, and product implementation Customers using affected product versions should apply security updates to mitigate the risk of exploit
AVEVA Pipeline Integrity Monitor: Four CVEs Expose Critical . . . Security Impact: As reported by CISA in advisory ICSA-26-253-01, AVEVA has disclosed four vulnerabilities in its Pipeline Integrity Monitor product that collectively pose a serious risk to critical manufacturing environments worldwide
AVEVA Knowledge and Support Center - Login Find supported solutions to common problems, product security guidelines, best product management practices, and more, provided by expert technical support engineers
AVEVA Pipeline Monitor: 4 CVEs Expose SCADA Systems | Smart Machines On September 10, 2026, CISA published advisory ICSA-26-253-01 disclosing four vulnerabilities in AVEVA Pipeline Integrity Monitor — industrial SCADA software widely used to manage pipeline operations across the energy and utilities sectors All versions up to 2025_SP1_P1 are affected
Security Central (Wonderware) - gcsresource. aveva. com Wonderware works closely with external Cyber Security groups to monitor Wonderware product vulnerability If a vulnerability is discovered, a bulletin is prepared with a solution and posted to the Security Central page, and to the Schneider Electric Software Cyber Security area
AVEVA Group Limited, Security Bulletin AVEVA recommends that organizations evaluate the impact of these vulnerabilities based on their operational environment, architecture, and product implementation